Local presence
EU-established regulatory interface

REGULATORY REPRESENTATION
Regulatory representation across EU and UK privacy, digital services, cybersecurity, data, AI and selected product frameworks.
Organisations operating across European and UK markets may need a representative under the regulatory frameworks applicable to their activities.
The legal role is not the same under every regime.
OSTRAI provides EU regulatory representation. UK GDPR Representative services are provided by PRIVACY MINDERS (UK) LIMITED. Scope assessment and the appropriate mandate depend on the relevant framework.
Representation requirements depend on where your organisation is established, what products or services you provide, how you operate in Europe and which regulatory frameworks apply.
A representative requirement under one regime does not automatically mean that another representative role also applies.
Representative scope check
Request representative scope assessmentThis initial scope check does not itself determine legal applicability. OSTRAI confirms the regulatory position before accepting an appointment.
EU PRESENCE
A regulatory representative can become the formal point through which authorities, individuals or other regulatory actors engage with an organisation established outside Europe.
Depending on the legislation, appointment can also determine regulatory jurisdiction, trigger registration or notification requirements, require access to compliance documentation, create cooperation duties or expose the representative to direct legal responsibility.
OSTRAI treats representation as part of the organisation's regulatory architecture rather than as a mailbox service.
EU-established regulatory interface
Role · Powers · Documentation · Boundaries
Authorities · Requests · Notices · Incidents
Changes · Compliance · Monitoring · Escalation
REPRESENTATIVE ROLES
European legislation uses several forms of representation.
The required role, mandate, duties and liability depend on the specific regulatory framework.
EU GDPR
A local representative for specified privacy-law purposes, including regulatory and data-subject contact functions.
DSA · NIS2 · Data Act · Data Governance Act · e-Evidence · selected digital regimes
A representative appointed under the relevant legislation to receive communications, cooperate with authorities or perform specified regulatory functions.
AI Act · CRA · selected product frameworks
A mandate-based role that can include verification, documentation, conformity, authority-cooperation or other statutory functions depending on the applicable legislation.
The roles are not interchangeable and a separate mandate, scope analysis and acceptance decision may be required under each framework.
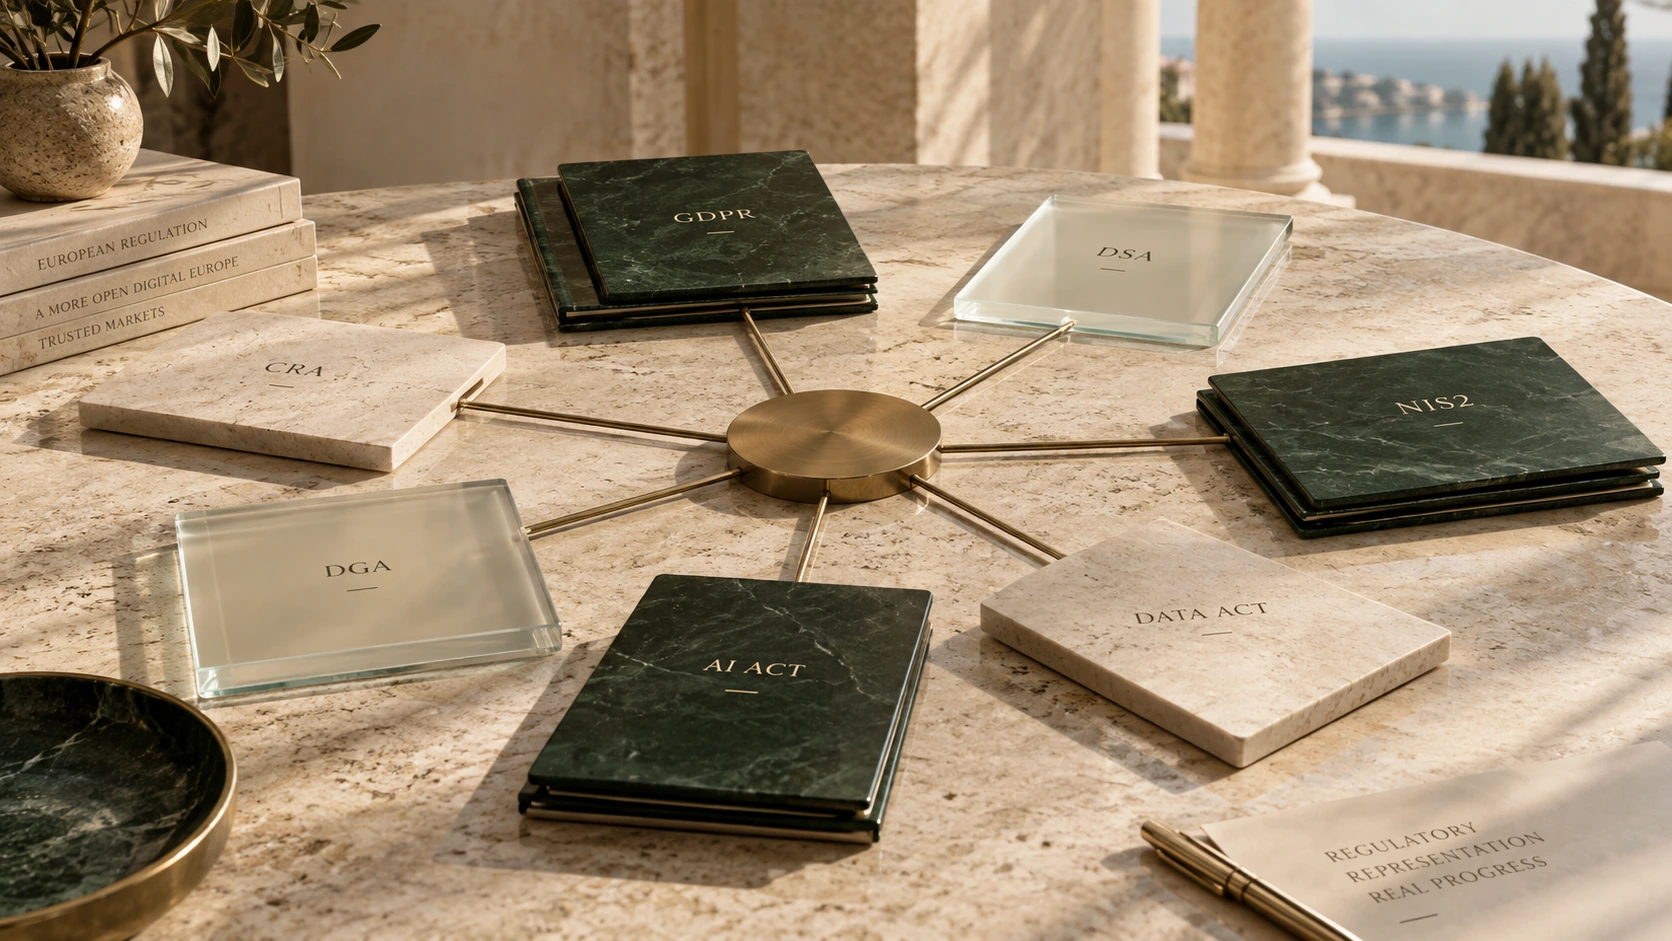
REPRESENTATION SERVICES
OSTRAI provides or assesses EU Regulatory Representation across European privacy, digital, cybersecurity, data and technology regulation.
Each appointment is scoped according to the applicable legal framework.
01 / Representation
Article 27 representation for organisations outside the European Union.
Organisations established outside the EU can be required to designate an EU representative where the GDPR applies to their processing through the offering of goods or services to individuals in the Union or the monitoring of their behaviour, subject to the applicable exemptions.
OSTRAI provides EU GDPR representation and acts as the designated regulatory interface under the agreed mandate.
02 / Representation
EU legal representation for non-EU intermediary service providers.
Providers of intermediary services without an establishment in the Union that offer services in the EU must designate a legal representative in a Member State where they offer those services.
The DSA legal representative can be addressed by competent authorities, the European Commission and the European Board for Digital Services in relation to DSA decisions and enforcement.
The role carries a materially different liability profile from GDPR representation.
OSTRAI therefore accepts DSA representative mandates only following regulatory scope and compliance review.
03 / Representation
NIS2 creates an EU representative requirement for specified non-EU digital and infrastructure service providers that offer services in the Union.
Relevant categories can include DNS and domain-name services, cloud computing, data centres, content delivery networks, managed service providers, managed security service providers, online marketplaces, search engines and social networking platforms.
The representative can become the regulatory and CSIRT contact point and can determine the Member State jurisdiction applicable to the non-EU entity.
Because NIS2 is implemented through national law, OSTRAI assesses the relevant Member State implementation as part of the appointment.
04 / Representation
Non-EU entities within the scope of the Data Act that make connected products available or offer relevant services in the Union can be required to designate an EU legal representative.
The representative can be addressed by competent authorities and must cooperate in demonstrating the organisation's Data Act compliance.
The location of the legal representative also affects the competent Member State.
OSTRAI combines the representative role with Data Act regulatory analysis where required.
05 / Representation
The Data Governance Act creates legal-representative requirements for certain non-EU data intermediation service providers and for qualifying non-EU entities seeking recognition as data altruism organisations.
The representative acts as a regulatory interface and cooperates with competent authorities regarding compliance with the applicable Data Governance Act requirements.
06 / Representation
CURRENT REQUIREMENT
Representation for receipt and compliance with European electronic-evidence orders.
The European e-Evidence framework requires relevant service providers offering services in the Union to designate an establishment or appoint a legal representative for the receipt of, compliance with and enforcement of orders used to obtain electronic evidence in criminal proceedings.
The EU e-Evidence representative framework is now operational for in-scope service providers.
For relevant non-EU providers, the legal representative is a substantive operational and enforcement role.
It can require the representative to receive and act on legally binding orders within strict procedural frameworks.
OSTRAI treats e-Evidence mandates as enhanced-risk appointments and undertakes an acceptance and operational-readiness review before appointment.
Potentially relevant services include:
07 / Representation
The AI Act creates authorised-representative requirements for specified providers established outside the Union, including certain providers of high-risk AI systems and general-purpose AI models.
The statutory duties differ according to the AI activity concerned.
They can include verification of documentation and conformity steps, retention of regulatory records, registration support and cooperation with the AI Office or national competent authorities.
OSTRAI accepts AI Act authorised-representative mandates only after assessing:
Authorised representative requirements where applicable to non-EU providers of high-risk AI systems.
Authorised representation for qualifying non-EU GPAI providers, subject to the applicable AI Act requirements and exemptions.
08 / Representation
CRA authorised representative appointments, subject to product-compliance and liability review.
The CRA permits manufacturers to appoint an EU authorised representative for specified tasks under a written mandate.
The CRA does not impose a universal authorised-representative requirement on every manufacturer established outside the Union.
Where OSTRAI is asked to accept a CRA authorised-representative mandate, appointment is subject to product-compliance and liability review.
Potential scope can include:
SPECIALIST REGIMES
Certain non-EU hosting service providers must designate an EU legal representative for receipt, compliance and enforcement of regulatory orders and decisions.
Because the representative may itself be exposed to liability under the Regulation, appointments are subject to enhanced review.
Additional European product or technology legislation can create authorised-representative, responsible-person or local economic-operator requirements.
OSTRAI considers selected mandates individually following regulatory scope, product-compliance, liability and insurance review.
This may include emerging or sector-specific technology frameworks where OSTRAI has the relevant regulatory capability and the appointment falls within its acceptance criteria.
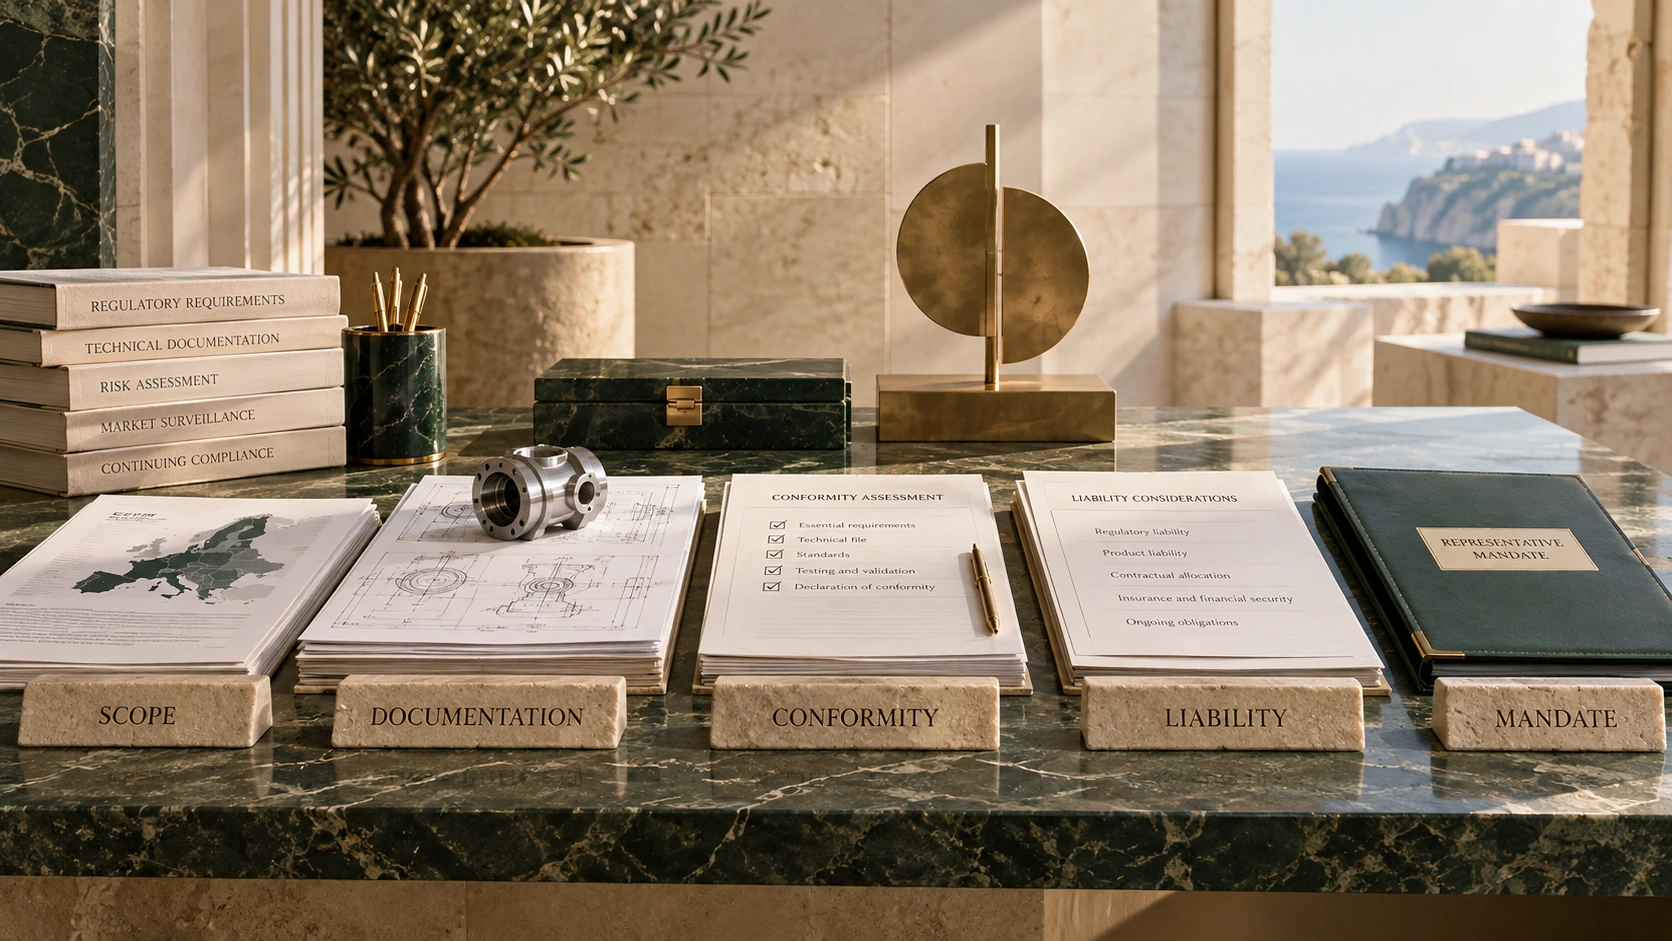
APPOINTMENT REVIEW
Representative roles carry different forms of responsibility.
In some regimes, the representative primarily acts as the local regulatory interface. In others, the representative can have substantive verification, compliance, enforcement or direct liability exposure.
Product-related appointments can create additional civil-liability considerations.
OSTRAI therefore applies different acceptance standards according to the mandate.
Typical examples
Subject to scope and client compliance review.
Typical examples
Review can include
Typical examples
Review can include
OSTRAI does not accept higher-liability or product authorised-representative appointments solely on execution of a mandate.
Compliance readiness and the risk profile are assessed first.
PRODUCT REPRESENTATION
Under the new EU Product Liability Directive, once applicable through national implementing law, an authorised representative of a manufacturer established outside the Union can be among the economic operators liable for damage caused by a defective product in specified circumstances.
Contractual indemnities can allocate risk between the parties but do not necessarily prevent claims by injured persons where statutory liability applies.
For that reason, OSTRAI treats product authorised representation differently from ordinary regulatory-interface representation.
Scope · Classification · Safety / cybersecurity
Requirements · Documentation · Assessment · Marking
Compliance maturity · Controls · History · Financial standing
Insurance · Indemnities · Recourse · Termination
WHY OSTRAI
A representative may be the first European contact point when a regulator, authority, individual or other stakeholder raises a compliance issue.
OSTRAI combines the appointment with regulatory understanding across the regimes in which it acts.
We determine whether the representative obligation applies before appointment.
Privacy · Cybersecurity · Data · Digital services · AI · Product regulation
Regulatory communications, requests, incidents and escalation.
Representation can be supported by broader regulatory implementation where required.
Higher-liability mandates are reviewed before OSTRAI accepts the appointment.
HOW IT WORKS
Establishment · Products · Services · Markets · Applicable regimes
Representation requirement · Jurisdiction · Applicable role
Documentation · Governance · Readiness · Risk
Scope · Powers · Responsibilities · Escalation · Terms
Regulatory notifications · Public details · Contact channels · Documentation
Requests · Authorities · Incidents · Changes · Regulatory monitoring
REPRESENTATIVE SCOPE CHECK
Tell us where your organisation is established, what you provide in Europe and which markets you serve.
OSTRAI will assess the likely representation framework and identify the information required before appointment.
Possibly. The requirement depends on the applicable regulation, your activities in Europe, whether you have an EU establishment and any exemptions under the relevant framework. OSTRAI assesses the position before appointment.
Potentially, but each role must be assessed separately. GDPR, DSA, NIS2, Data Act, AI Act and other frameworks can impose different location, mandate, duty, jurisdiction and liability requirements.
No. A GDPR representative is the designated local regulatory interface for qualifying non-EU organisations. A DPO performs an independent advisory and monitoring function. The roles are legally distinct.
Where both regimes require representation, they are separate appointments. The EU GDPR Representative must satisfy the EU GDPR requirements and the UK GDPR Representative must satisfy the UK GDPR requirements. UK GDPR Representative services are provided through PRIVACY MINDERS (UK) LIMITED, a UK-established company, separately from OSTRAI's EU Regulatory Representation practice.
It depends on the regulatory framework. Some regimes leave primary responsibility with the represented organisation, while others can impose direct, joint or mandate-based responsibilities on the representative. OSTRAI assesses the liability position before accepting higher-risk appointments.
No. Representation fulfils the representative requirement where applicable. The represented organisation remains responsible for its substantive regulatory obligations, together with any separate duties imposed directly on the representative.
EU REGULATORY REPRESENTATION
OSTRAI helps non-EU organisations determine which representative obligations apply, establish the appropriate mandate and maintain an effective regulatory interface across European privacy, digital, cybersecurity, data, AI and selected product frameworks.