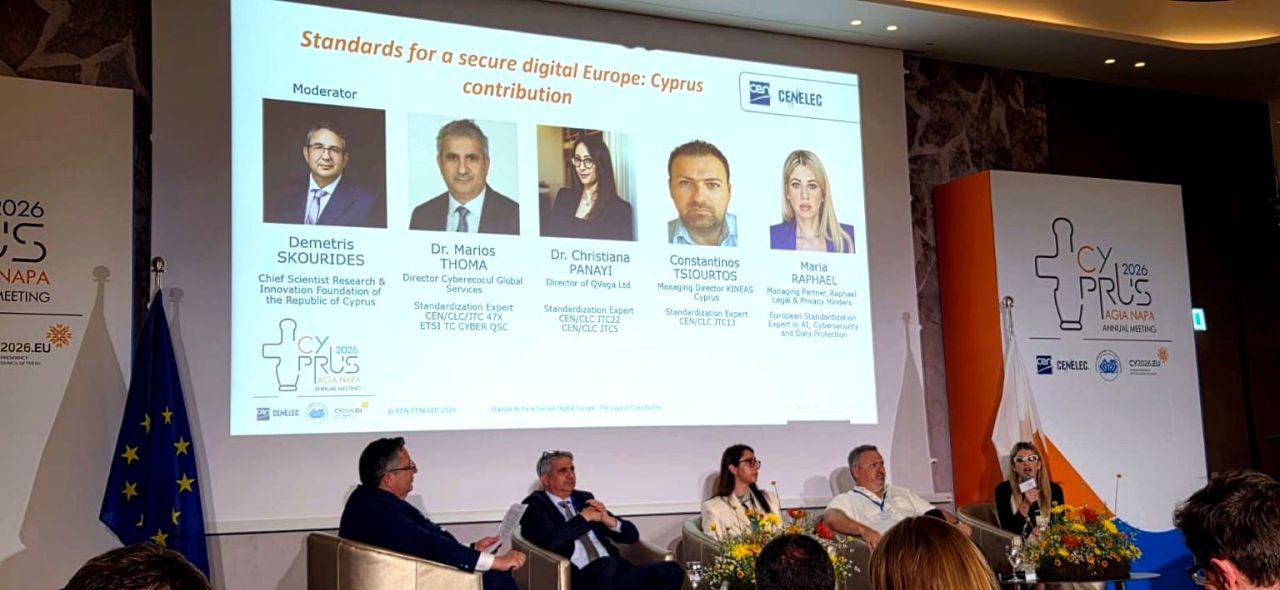
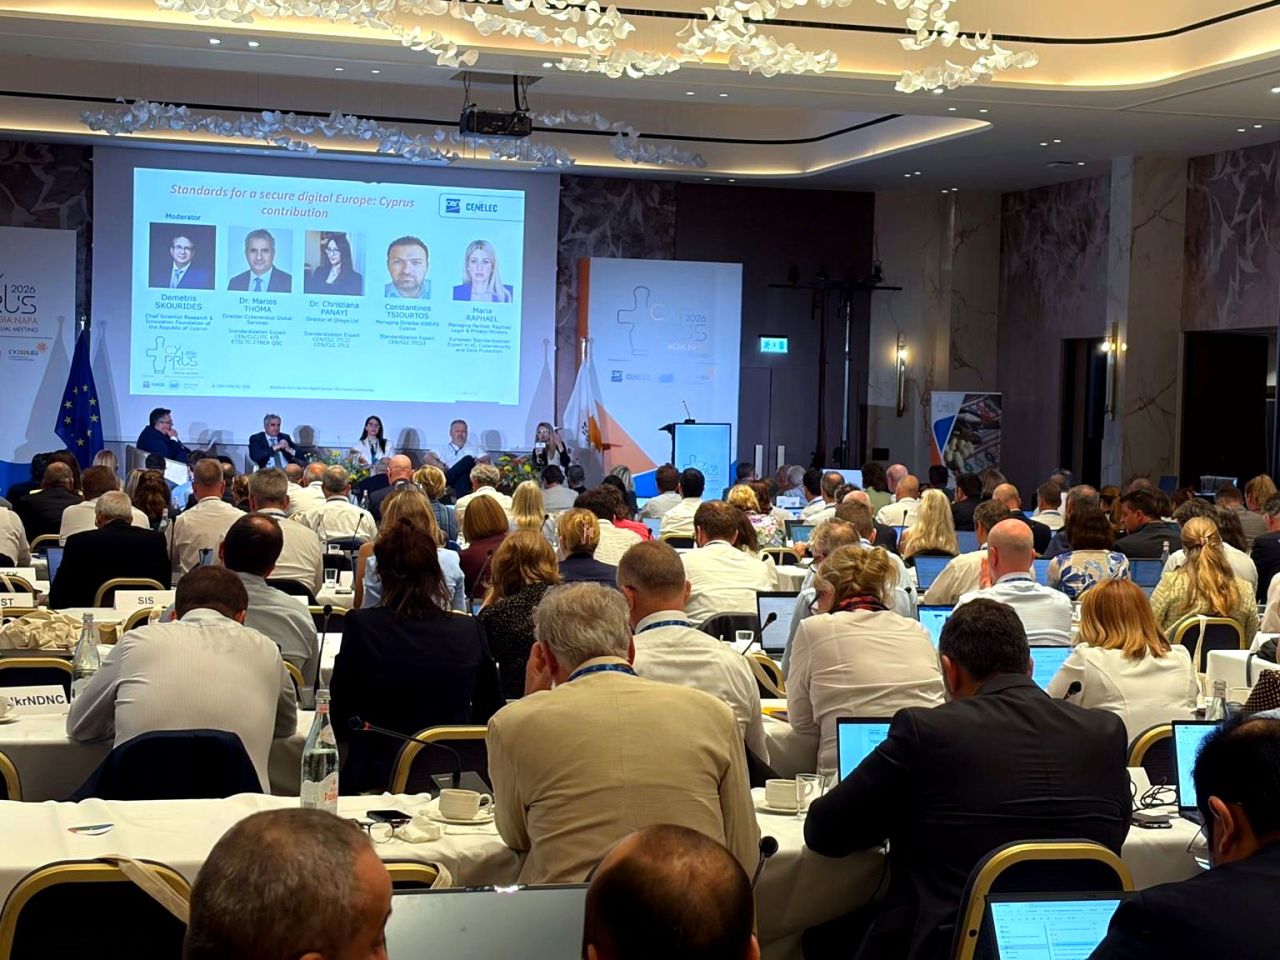
During the CEN and CENELEC Annual Meeting 2026 in Agia Napa, Cyprus, Maria Raphael participated in the panel “Standards for a Secure Digital Europe: The Cyprus Contribution”, hosted by the Cyprus Organisation for Standardisation (CYS).
The Annual Meeting brought together the leadership and members of the European standardisation community, representatives of European institutions, National Standardisation Bodies, public-sector officials and experts from across Europe.
The panel examined the growing strategic role of standards in supporting Europe’s digital transformation, cybersecurity, innovation, resilience and technological sovereignty.
The discussion was moderated by Demetris Skourides, Chief Scientist for Research, Innovation and Technology of the Republic of Cyprus.
Maria Raphael drew on her involvement in European standardisation and, in particular, the Cyber Resilience Act standardisation journey; from discussions surrounding the legislative proposal and the standardisation request to participation in work on horizontal and vertical European standards.
The discussion raised a broader question:
As Europe becomes increasingly dependent on standards to implement regulation, is the standardisation system being given the conditions it needs to succeed?
European standardisation at a turning point
The role of European ICT standardisation is changing.
Standards have traditionally provided common technical specifications, terminology, interoperability frameworks and methods for demonstrating technical performance.
Increasingly, however, they are also expected to support implementation of major European regulatory initiatives.
The panel explored this shift across areas including:
- the Cyber Resilience Act;
- the AI Act;
- cybersecurity;
- trusted supply chains;
- conformity assessment;
- quantum technologies; and
- Europe’s broader digital and innovation agenda.
A recurring theme was that standards are no longer viewed solely as technical documents.
They are increasingly recognised as strategic instruments that can enable innovation, create trust, strengthen competitiveness and translate European policy objectives into operational frameworks.
The standardisation paradox
One of the concepts Maria Raphael introduced during the discussion was what she described as the “standardisation paradox”.
Europe is becoming increasingly dependent on standards to support implementation of its regulatory frameworks.
At the same time, complementary mechanisms are emerging alongside traditional standardisation processes.
That development suggests a growing hesitation to rely on standardisation alone as the sole mechanism for both technical specification development and the implementation of public-policy objectives.
The paradox is therefore that standards are becoming more important precisely while policymakers are also exploring mechanisms that reduce exclusive reliance on them.
This raises difficult questions.
If European regulation increasingly depends on standards, what conditions are required for the standards system to deliver effectively?
And where complementary mechanisms are introduced, how should they interact with the established European standardisation system?
At a time when Europe is becoming increasingly dependent on standards, it is also becoming less willing to rely on standardisation alone.
What the CRA standardisation journey teaches
The Cyber Resilience Act provides a particularly useful case study.
Maria Raphael reflected on her involvement throughout the CRA standardisation journey; from discussions surrounding the legislative proposal and the standardisation request to the drafting of horizontal and vertical European standards.
One of the most important lessons emerging from that experience is that the central challenge is not simply how to make standardisation faster.
The deeper question is how to create the conditions that allow standardisation to succeed.
Those conditions include:
- the timing of stakeholder involvement;
- the information available when standards work begins;
- the flexibility available to standards developers;
- the interaction between horizontal and vertical deliverables;
- dependencies between different standards;
- the complexity of the standardisation programme; and
- the relationship between regulatory deadlines and technical development.
Large regulatory standardisation programmes can create chains of dependency.
A delay or change in one element may affect several others.
The challenge is therefore not only speed.
It is designing a standardisation process that is capable of producing coherent, technically credible and implementable outcomes within the regulatory environment in which those standards will operate.
Standards need the conditions to succeed
The CRA experience points to a broader policy lesson.
If legislation is increasingly designed on the assumption that standards will support implementation, the conditions under which those standards are produced become part of regulatory effectiveness itself.
Standardisation cannot simply be treated as a downstream technical exercise that begins once legislation is complete.
Early engagement matters.
So does clarity about regulatory objectives.
Standards developers also need enough technical flexibility to develop workable solutions rather than merely restating legislative language.
At the same time, policymakers need visibility into whether the standardisation programme remains capable of delivering what the regulation expects.
The effectiveness of European digital regulation can therefore depend, in part, on the effectiveness of the standards-development environment that supports it.
Standards are becoming strategic infrastructure
The discussion also reflected a wider change in how European standardisation is understood.
Standards increasingly sit at the intersection of:
- regulation;
- innovation;
- cybersecurity;
- industrial policy;
- market access;
- interoperability;
- resilience; and
- technological sovereignty.
They can help establish common technical expectations across the European market.
They can also reduce fragmentation and provide a common basis for conformity assessment, implementation and trust.
For businesses, this means standardisation can influence not only technical design but also regulatory strategy and market planning.
Understanding European digital regulation therefore increasingly requires understanding the standards that support its implementation.
Beyond the Cyber Resilience Act
Although the CRA provided an important reference point for Maria Raphael’s contribution, the panel considered a wider set of issues affecting Europe’s digital future.
The discussion included artificial intelligence, cybersecurity, trusted supply chains, conformity assessment and quantum technologies.
These areas illustrate how European standardisation increasingly operates across regulatory boundaries.
A standard developed within one technical context may support several policy or market objectives.
Similarly, organisations operating in emerging technologies may need to understand several regulatory and standardisation frameworks at the same time.
The future of ICT standardisation will therefore depend partly on whether the European system can maintain coherence across increasingly interconnected regulatory programmes.
CSA2 as a lens on the future of European standardisation
One of the most engaging moments of the discussion came during audience questions, when the proposed revision of the Cybersecurity Act (CSA2) was raised.
The question provided a useful lens through which to examine broader developments affecting European standardisation.
It illustrated how the relationship between legislation, certification, standards and other implementation mechanisms continues to evolve.
As Europe introduces new regulatory instruments and revises existing ones, the institutional architecture supporting technical implementation is likely to become increasingly important.
The future question is therefore not only:
What should European regulation require?
It is also:
Which technical and institutional mechanisms are best placed to make those requirements workable in practice?
Cyprus’s contribution to European standardisation
The panel also highlighted Cyprus’s growing contribution to European and international standardisation.
Hosted by the Cyprus Organisation for Standardisation, the discussion brought together Cypriot experts actively participating in standards work across cybersecurity, artificial intelligence, trusted technologies, conformity assessment and emerging technologies.
Cyprus’s contribution does not depend on the size of its domestic market.
It depends on active participation.
Experts participating through national delegations, technical committees and working groups can contribute directly to the standards that shape the European regulatory and technological environment.
The Annual Meeting demonstrated how that participation can contribute to a secure, interoperable and resilient digital Europe.
Where European ICT standardisation goes next
The future of European ICT standardisation will be shaped by competing pressures.
Europe needs standards that are trusted, technically credible and developed through an inclusive system.
It also needs implementation mechanisms capable of responding to rapidly evolving technologies, markets and regulatory priorities.
That creates pressure for standards to become faster and more responsive without losing the qualities that make the European system valuable.
The “standardisation paradox” captures that tension.
Standards are becoming indispensable to digital regulation.
At the same time, their expanding policy role is creating pressure for complementary mechanisms and alternative implementation pathways.
Managing that tension will be one of the central challenges facing European standardisation.
The CRA experience suggests that the answer is unlikely to be simply “faster standards”.
The more important task is to create a system in which standardisation has the information, participation, flexibility and institutional conditions needed to succeed.
For organisations navigating European digital regulation, one conclusion is already clear:
understanding regulation increasingly requires understanding the standards through which that regulation becomes operational.